Who needs CMMC Level 1?
Start with the solicitation, contract, and subcontract flowdowns. CMMC Level 1 can apply when a defense contractor or subcontractor handles FCI on its information systems and the procurement requires Level 1 status. Company size alone does not determine the requirement. A small supplier can have information-protection responsibilities when its systems handle nonpublic contract information.
FCI generally means nonpublic information provided by or created for the government under a contract to develop or deliver a product or service. Publicly available government information and simple transactional information needed to process payments are excluded. See the definition in FAR 52.204-21 and the contractor decision guide.
Hypothetical example: a supplier receives nonpublic delivery instructions for a defense contract through company email. The practical first step is to determine the information’s classification and contractual requirements, then trace where those instructions are stored and shared. Do not assume every contract attachment is FCI or CUI without checking.
What are the 15 CMMC Level 1 requirements?
The 15 basic safeguards come from FAR 52.204-21. They address who can access systems, what authorized users can do, identity verification, media disposal, physical access, network boundaries, and system integrity. The 15-safeguard guide explains each requirement in plain language.
| Area | Practical question | Possible supporting record |
|---|---|---|
| Access and identity | Can only approved users and devices access the environment? | Account inventory and access review |
| Physical protection | How are visitors and physical access handled? | Visitor records and access procedures |
| Media disposal | How is FCI removed before equipment leaves your control? | Sanitization or destruction record |
| System integrity | How are vulnerabilities, malicious code, and required updates addressed? | Patch, protection, and scanning records |
These are examples, not a substitute for the assessment objectives. A policy describing a safeguard does not prove that it operates. Review actual settings, records, and practices against the applicable objectives.
Is Level 1 a certification or a self-assessment?
The precise status is Final Level 1 (Self). Level 1 uses the organization’s self-assessment, rather than a third-party C3PAO certification assessment. Under 32 CFR 170.15, all Level 1 requirements must be MET. There is no conditional Level 1 status based on a plan of action and milestones (POA&M).
An outside adviser may help organize or review preparation, but your organization remains responsible for its assessment and affirmation. Buying software, downloading policies, or receiving a consultant’s checklist does not itself establish CMMC status.
What does the annual assessment involve?
- Confirm scope. Identify the systems that process, store, or transmit FCI and apply the official scoping rules. Document relevant people, facilities, and providers.
- Examine implementation. Use the required assessment objectives to review the safeguards and supporting evidence.
- Close gaps. Complete and verify missing safeguards before concluding that all requirements are MET.
- Enter and affirm the result. Prepare the correct scope, CAGE codes, and assessment information for SPRS. The authorized senior representative completes the required affirmation.
- Maintain the environment. Repeat the self-assessment annually, keep affirmation current, and retain assessment evidence for six years from the CMMC Status Date.
Use the readiness checklist to organize preparation and the SPRS preparation guide before working in the government system.
How is Level 1 different from Level 2?
Level 1 addresses FCI through the 15 FAR safeguards. Level 2 addresses Controlled Unclassified Information (CUI) through 110 requirements in NIST SP 800-171 Revision 2 under the current CMMC rule. Do not choose Level 1 merely because it appears easier; information and contract requirements determine the applicable path. Our Level 1 versus Level 2 comparison explains the distinction.
Rollout checked October 25, 2026: the DoD CMMC program office says Phase II was suspended on July 13, 2026, with implementation paused in Phase 1. Phase I self-assessment requirements remain in place. Check current official guidance and your procurement instead of relying on older rollout calendars.
How CMMC Pulsar and Federal Bid Partners help
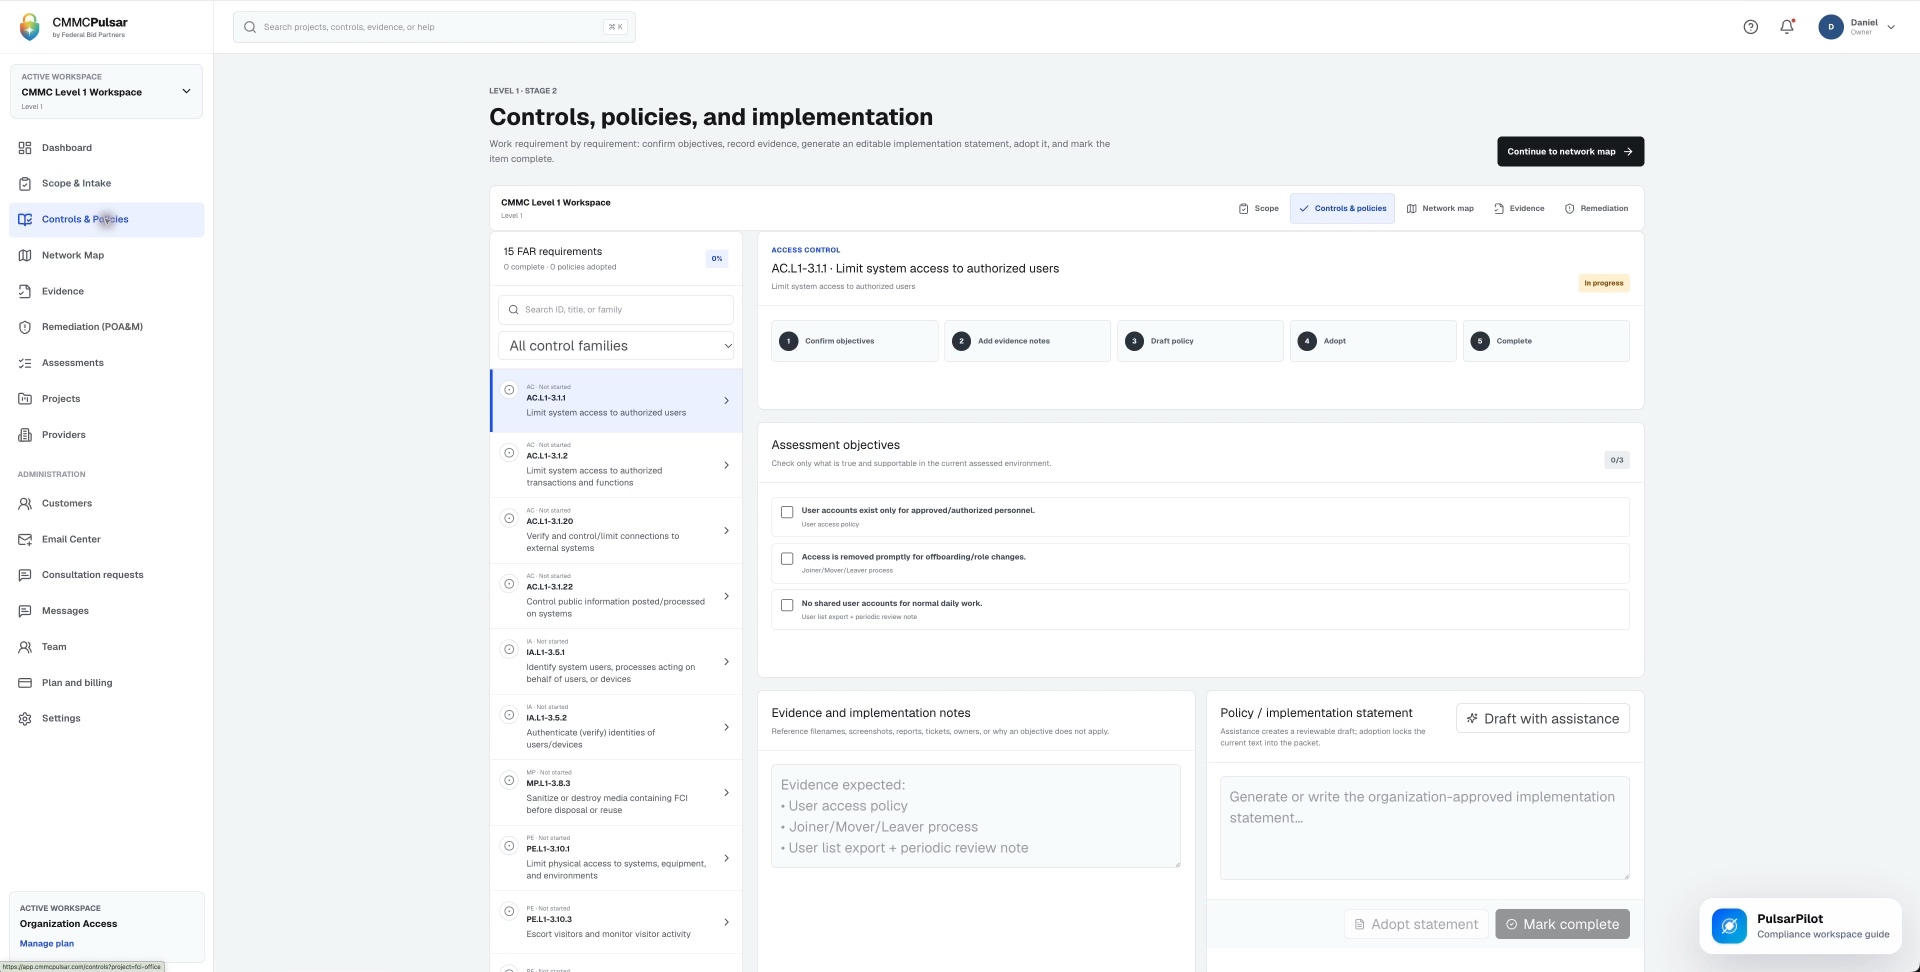
CMMC Pulsar is readiness software developed by Pulsar Technology LLC, a sister company of Federal Bid Partners (FBP). It helps connect scope, requirements, implementation statements, evidence, and open work in one workspace. FBP provides a team to discuss readiness scope and support needs.
A useful starting point is one real business workflow: list who handles FCI, where it goes, which safeguards apply, and what remains unresolved. Bring those facts into the workspace before generating documentation. For budgeting, read CMMC Level 1 cost and timeline; for the relationship between people and software, see the FBP and CMMC Pulsar guide.
Frequently asked questions
Does every federal contractor need CMMC Level 1?
No. CMMC is a DoD program with specific applicability rules, exceptions, contract requirements, and implementation phases. Review the actual solicitation or contract and any subcontract flowdowns.
Can I complete a CMMC Level 1 self-assessment myself?
Level 1 is an organizational self-assessment. Your team needs enough knowledge of its environment and the assessment objectives to support its conclusions. Outside assistance is optional; it does not transfer the organization’s responsibility.
Can I use a POA&M for missing Level 1 safeguards?
No. Level 1 does not permit a POA&M for achieving Final Level 1 (Self). Resolve missing requirements before reporting all requirements as MET.
Does CMMC Pulsar submit my official SPRS result?
CMMC Pulsar helps organize readiness work and supporting records. Your authorized users complete the official assessment-result and affirmation workflow in SPRS.
Sources & further reading
- FAR 52.204-21: FCI definition and 15 safeguards ↗
- 32 CFR 170.15: Level 1 assessment and evidence retention ↗
- 32 CFR 170.19: assessment scoping ↗
- 32 CFR 170.22: affirmation requirements ↗
- DoD CMMC program overview and current implementation ↗
- SPRS CMMC guidance and training ↗
Published October 25, 2026. Official sources checked October 25, 2026. General information and practical planning examples; confirm the requirements that apply to your organization.